GAID 2025
Record of processing (RoPA)
What personal data you hold, why, on what lawful basis and who you share it with. Upload a vendor contract and Izini drafts the entry for you to approve.
 Izini
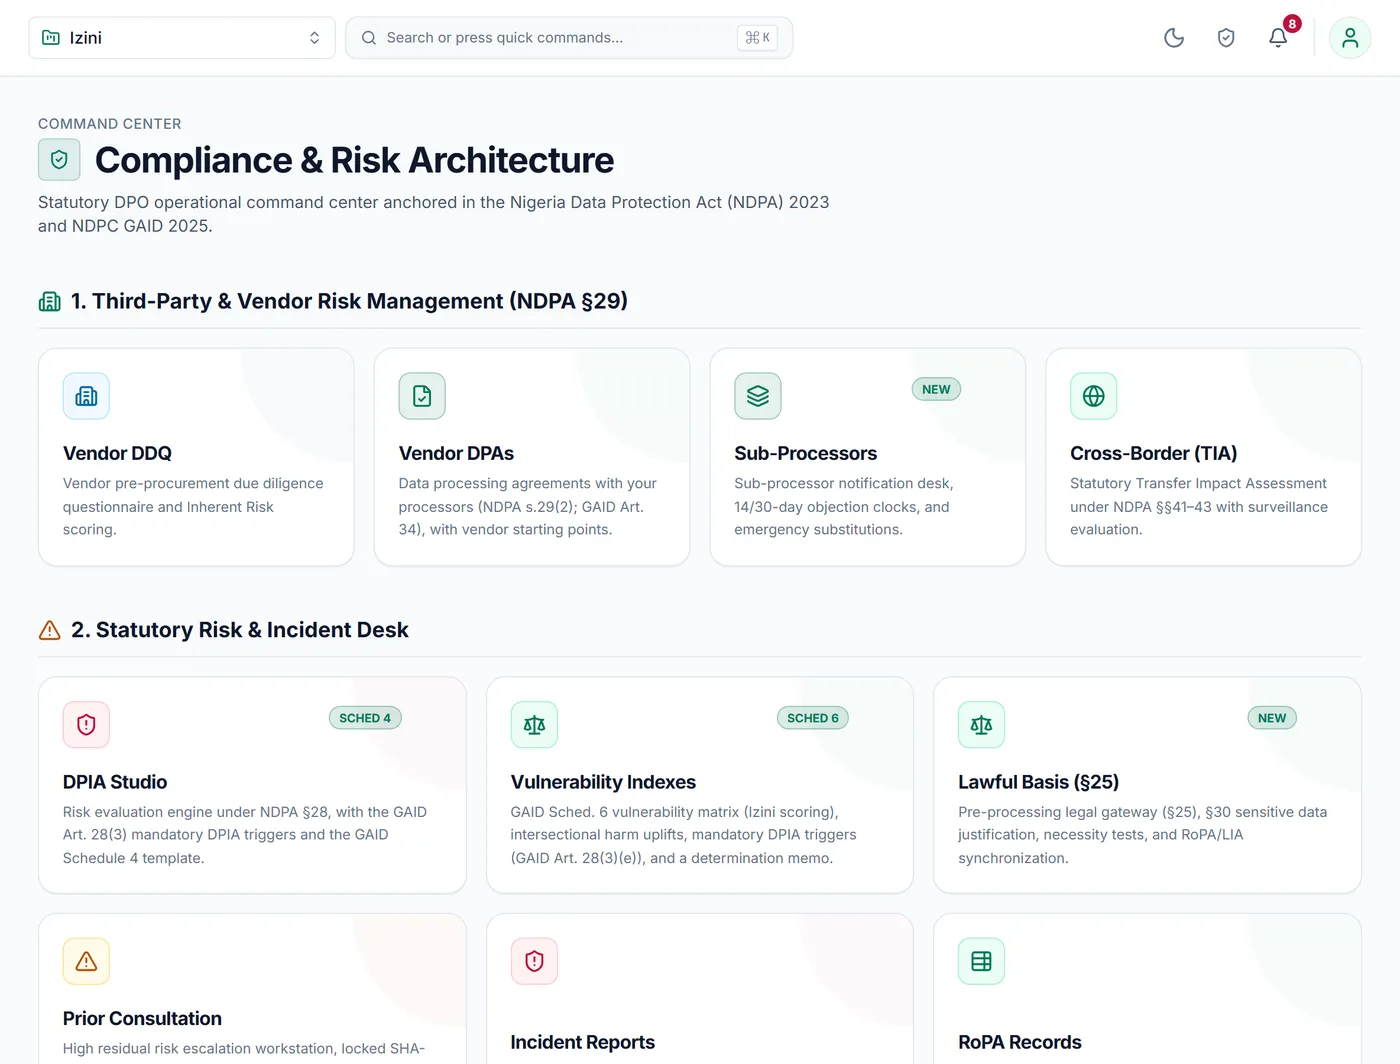 Everything Izini does →Every module, grouped by area, with the part of the law it covers.
Most compliance programmes fail on paperwork: the controls exist, but nobody can show them. Izini keeps your record of processing, impact assessments, risk register and privacy policy in one place, and drafts much of it for you to approve.
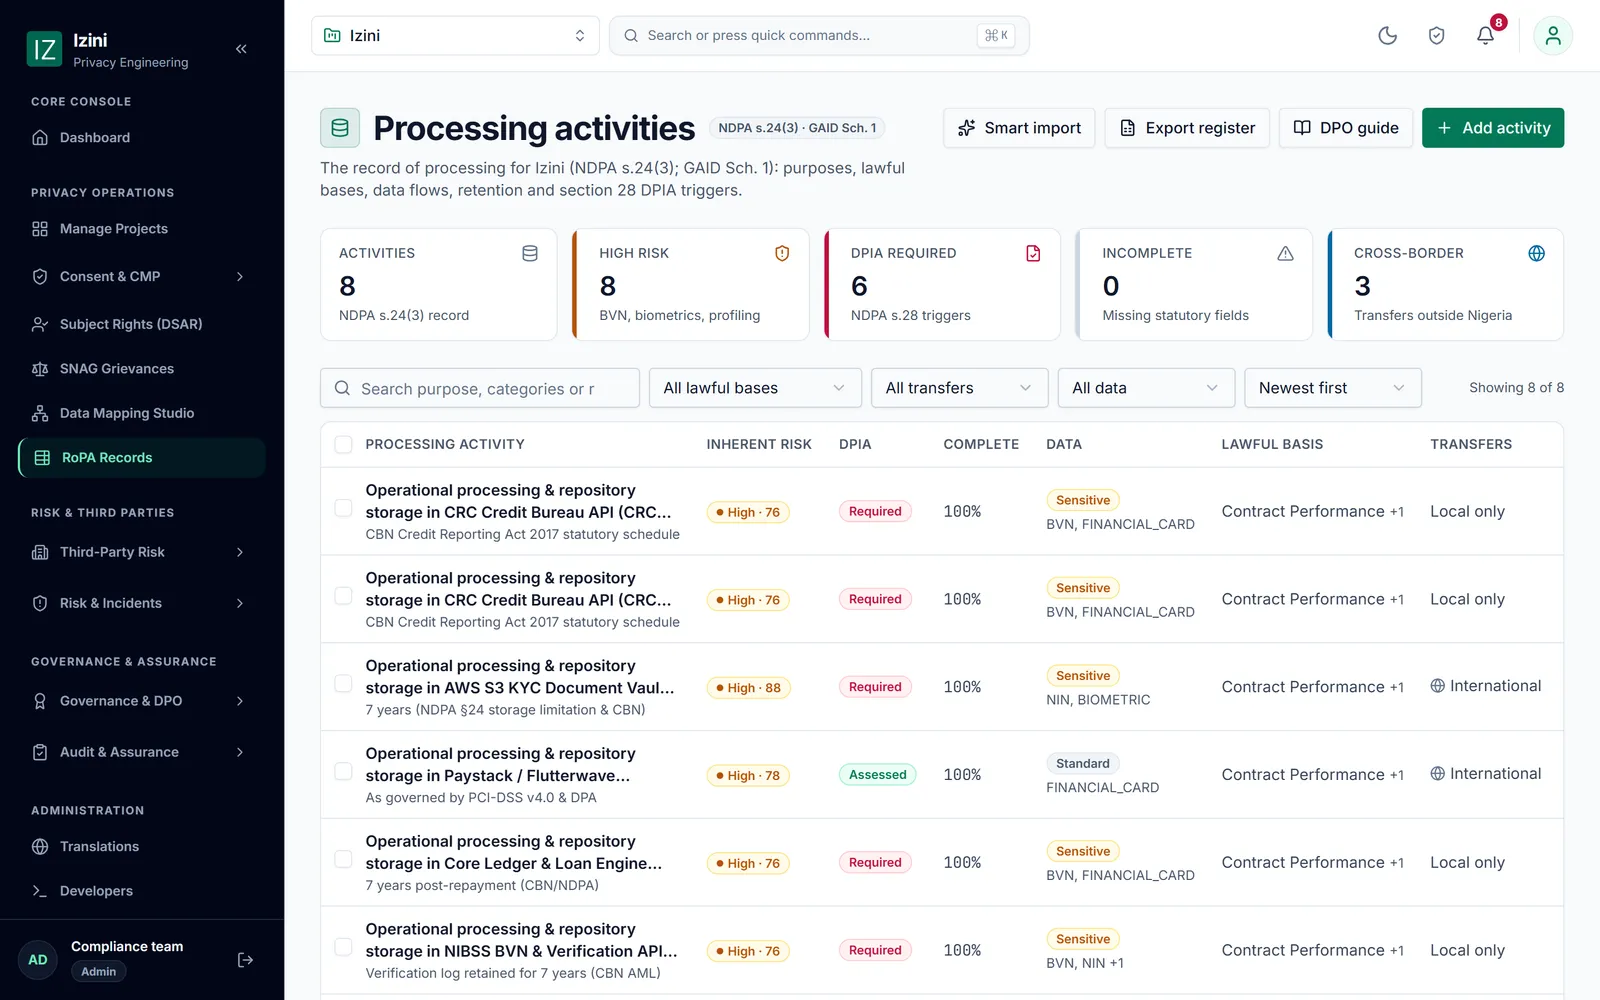
Upload a vendor contract and Izini drafts the record entry for you to check.
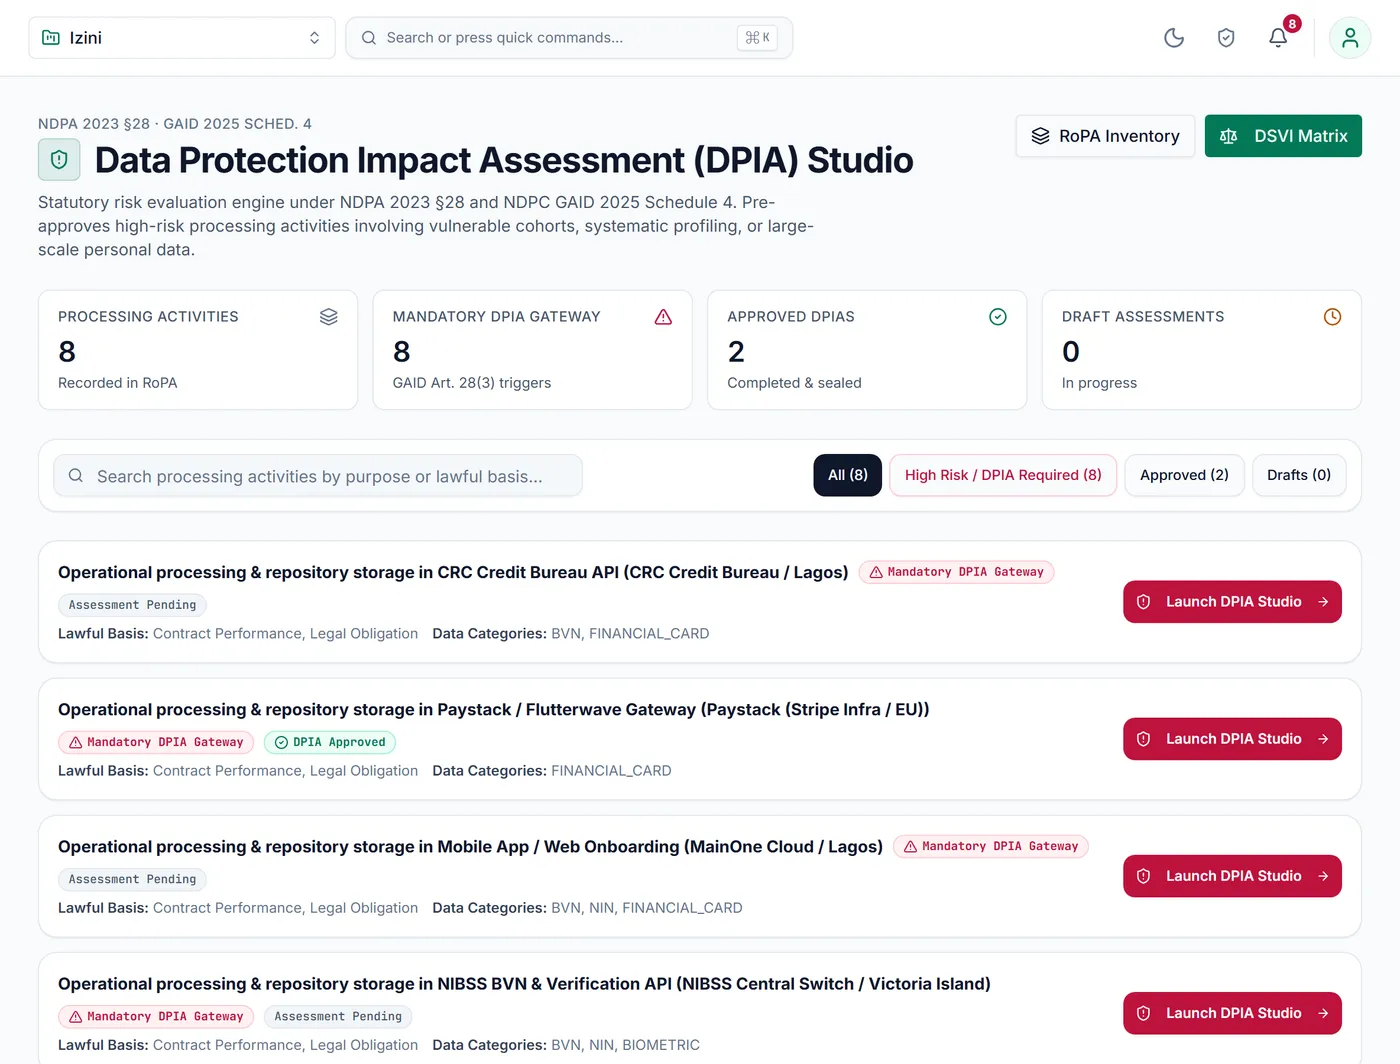
Activities that need an impact assessment are flagged automatically.
Your privacy policy is published at its own link and revised when things change, with your approval.
Izini lists the activities that need an assessment, walks you through it and tells you when you must consult the NDPC before going ahead.
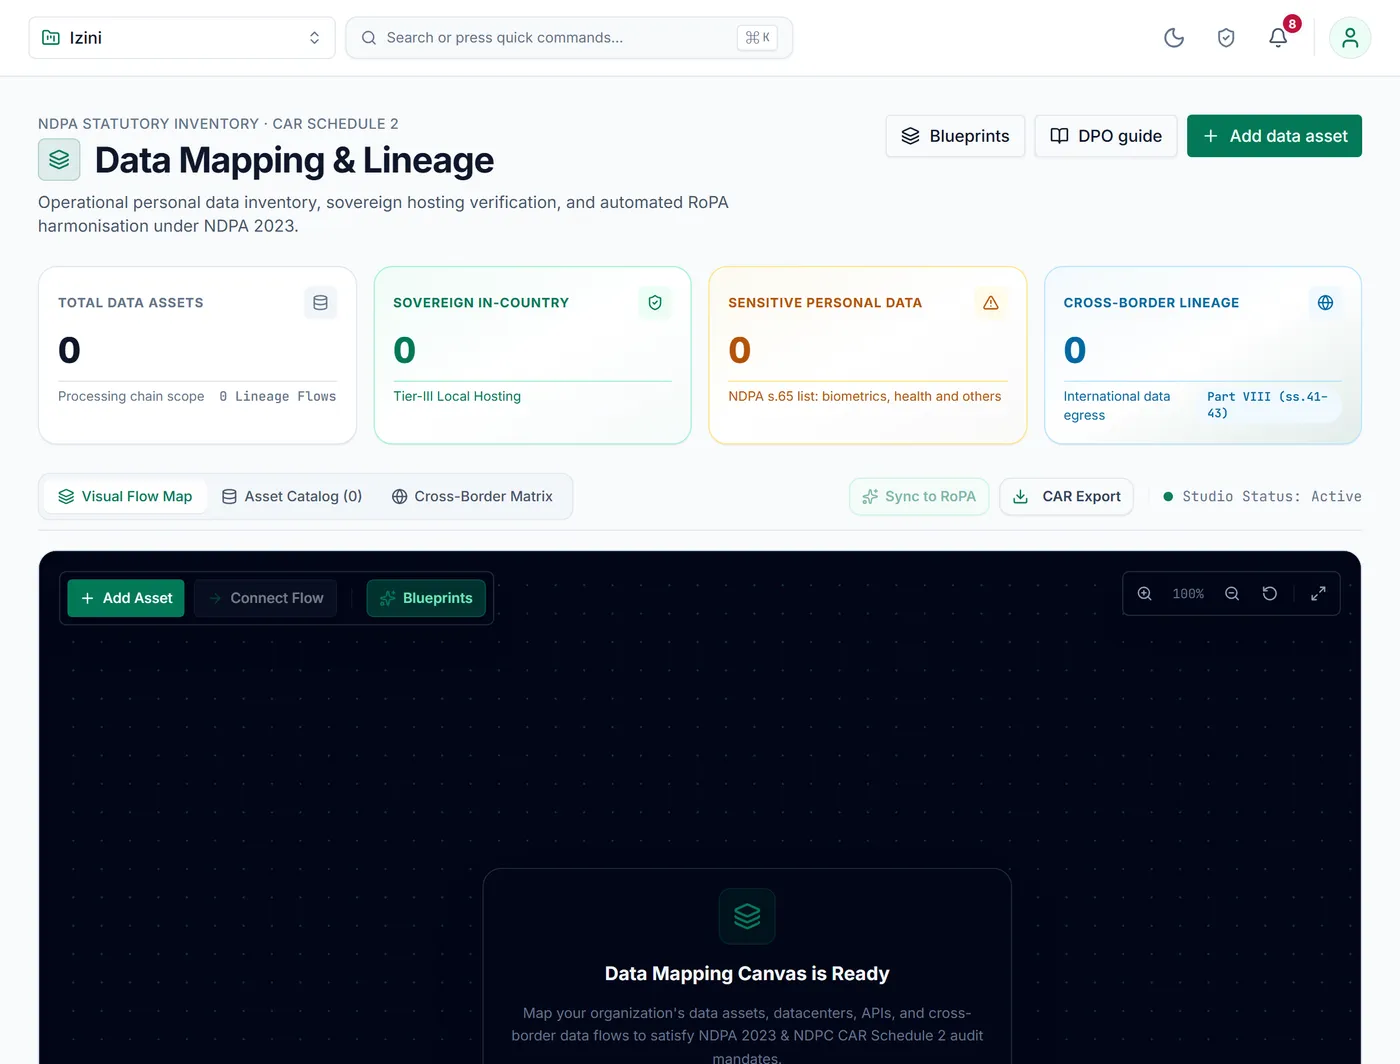
A map of the systems that hold personal data and the flows between them, including which keep it in Nigeria and which send it abroad.
Generated from what you actually do, hosted at its own link, with version history. When your processing changes, Izini drafts the revision for you to approve.
What personal data you hold, why, on what lawful basis and who you share it with. Upload a vendor contract and Izini drafts the entry for you to approve.
When risk stays high after your safeguards, Izini prepares the consultation file for the NDPC from the impact assessment.
For every activity, which lawful basis you rely on and why, ready for your annual audit.
Records the balancing test when you rely on legitimate interests, the basis regulators question most.
A 5×5 register of privacy risks with likelihood, impact, treatment plans and owners, so decisions are written down rather than remembered.
The technical and organisational measures that protect personal data, with a schedule for checking they still work.
Assess whether the people whose data you hold include children, patients or others who need extra care, and weight your safeguards to match.
A new feature that touches personal data cannot ship until its privacy review is approved. Works with GitHub, GitLab and other pipelines.
When your cookies or records of processing change, Izini drafts the changes your privacy policy needs and sends them to your DPO to approve.
What the NDPA asks of you in this area, and the evidence Izini keeps for each requirement.
| What the law asks | Where it comes from | What Izini keeps for you |
|---|---|---|
| Have a lawful basis for each use of data | NDPA s.25 | A lawful basis entry for every activity, with the reasoning |
| Assess high-risk processing first | NDPA s.28 | The impact assessment, its score and any consultation with the NDPC |
| Tell people how their data is used | NDPA s.27 | The published privacy policy and its versions |
| Protect the data you hold | NDPA s.39 | Your security measures and the checks that they still work |
In a 30-minute demo we look at your own website, show you what the NDPA expects of an organisation like yours, and answer your questions about setup and price.