NDPA s.34s.38
Request register
Requests to see, correct, delete or move personal data land in one register with an identity check, a due date and a full history.
 Izini
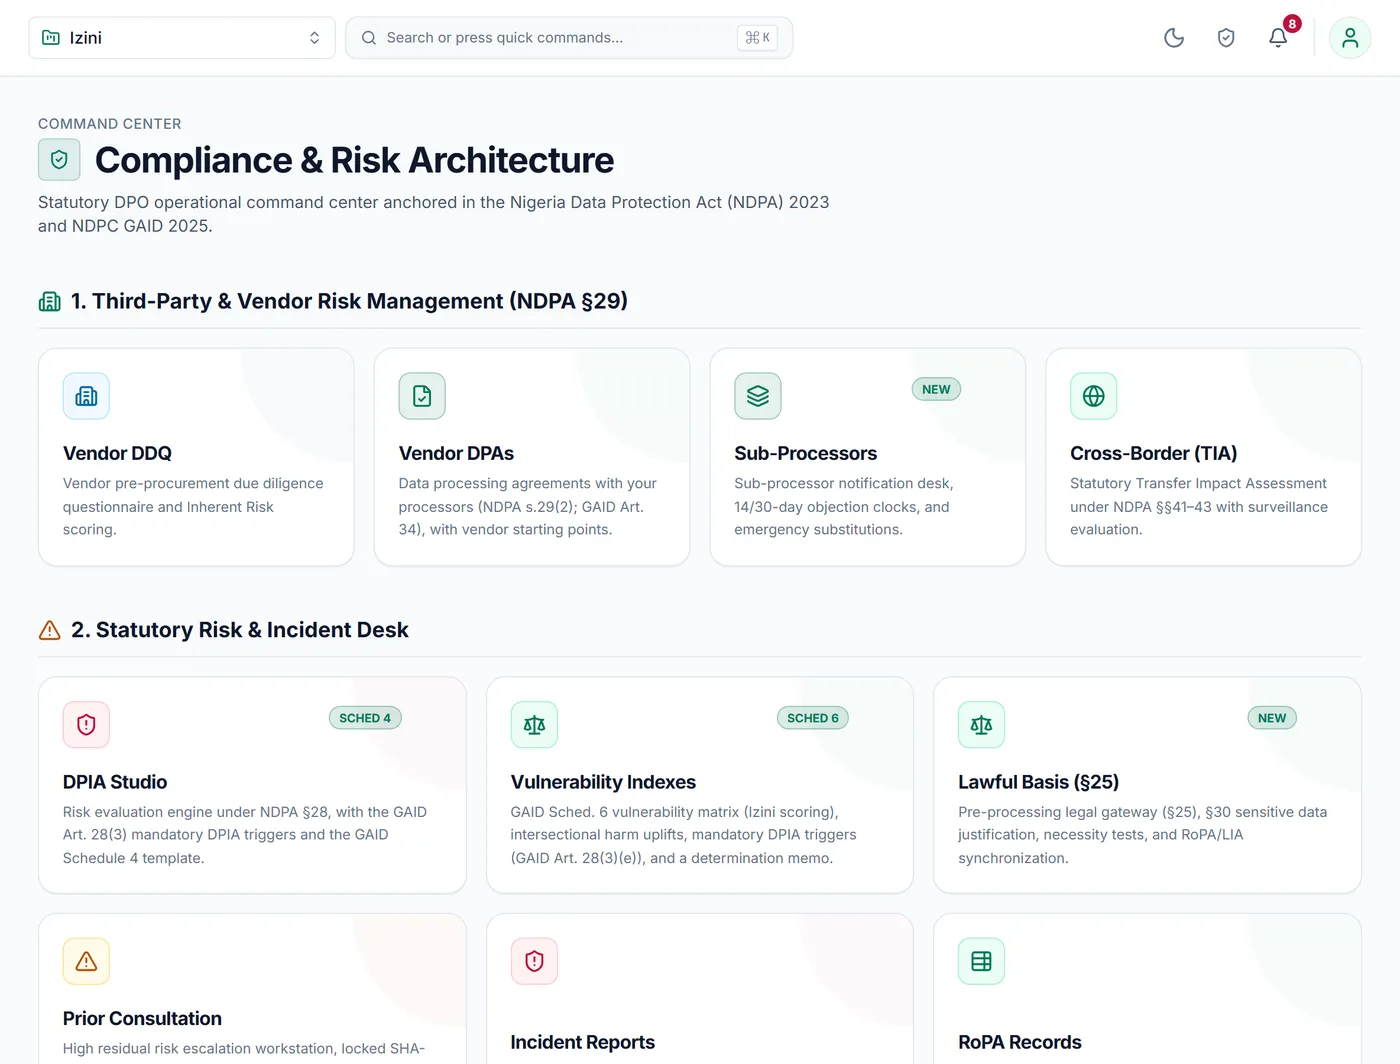 Everything Izini does →Every module, grouped by area, with the part of the law it covers.
Customers can ask to see, correct, delete or move the data you hold about them, and the NDPA expects you to respond without unreasonable delay. Izini opens a case for each request, checks who is asking and reminds you before it runs late.
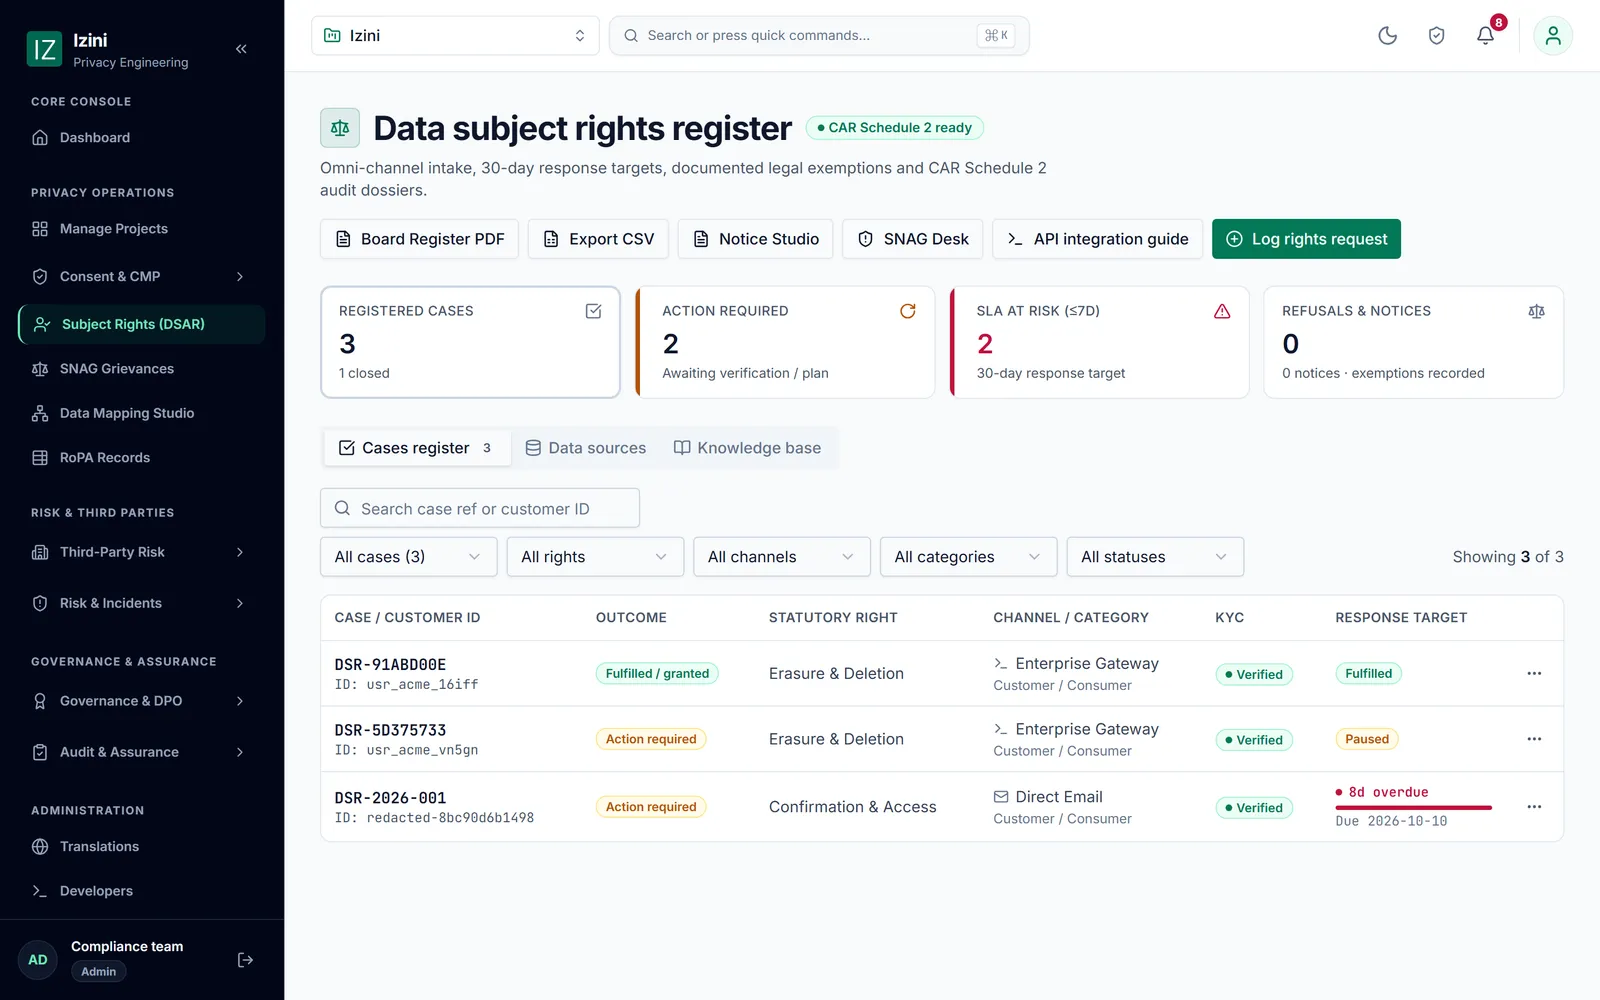
Requests from your banner, website, email and systems all land in one register.
An identity check comes before anything is released.
Each case keeps a full history for complaints and your annual audit.
A desk for privacy complaints, with ready-made scenarios and a record of how each one was handled. Many complaints end here instead of at the NDPC.
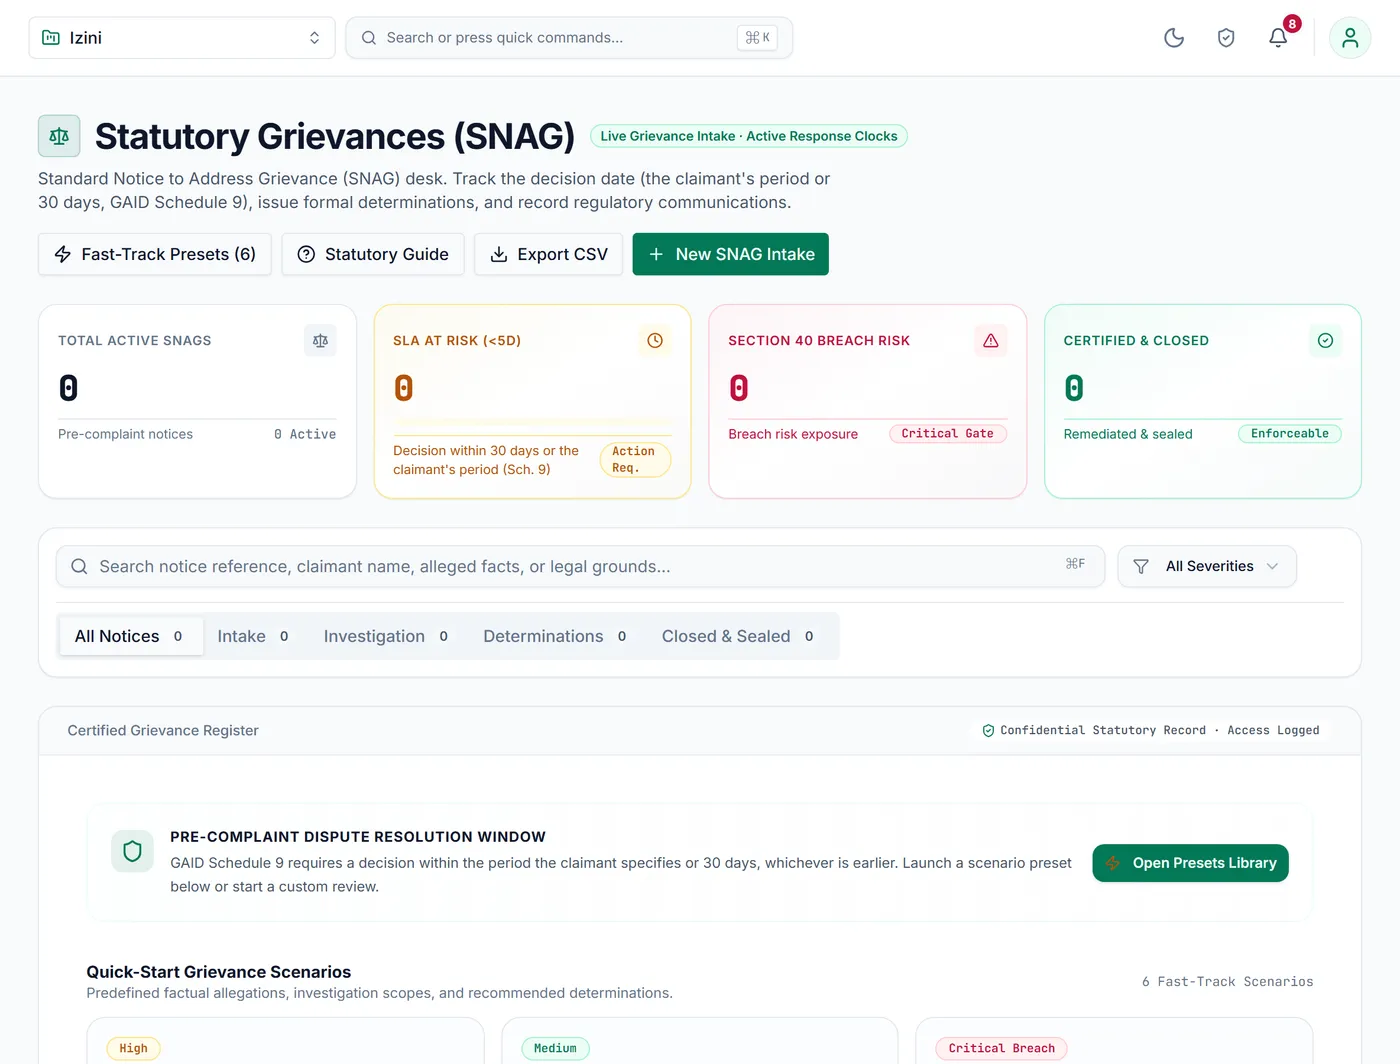
Requests to see, correct, delete or move personal data land in one register with an identity check, a due date and a full history.
Requests can come from your cookie banner, your website, email or your own systems, and all of them open a case in the same register.
Connect the systems that hold customer data, so each request shows your team where to look and what to remove.
What the NDPA asks of you in this area, and the evidence Izini keeps for each requirement.
| What the law asks | Where it comes from | What Izini keeps for you |
|---|---|---|
| Give people access to their data, and correct or delete it | NDPA s.34 | The request, the identity check and the response |
| Let people take their data elsewhere | NDPA s.38 | Portability requests in the same register |
| Respond without unreasonable delay | NDPA s.34 | Dates for every step, tracked against a 30-day target |
The NDPA does not set a fixed number of days for a response. Izini's 30-day target is an internal benchmark you can show as evidence of a prompt reply.
In a 30-minute demo we look at your own website, show you what the NDPA expects of an organisation like yours, and answer your questions about setup and price.