 Izini
 Everything Izini does →
Connect compliance to the systems you already run.
Izini has a documented REST API, signed webhooks and mobile SDKs, so your apps, backend, ticketing and reporting tools take part in compliance instead of someone copying data between screens.
Live API keys and webhooks come with every paid plan. The Free plan and the trial can create test keys.
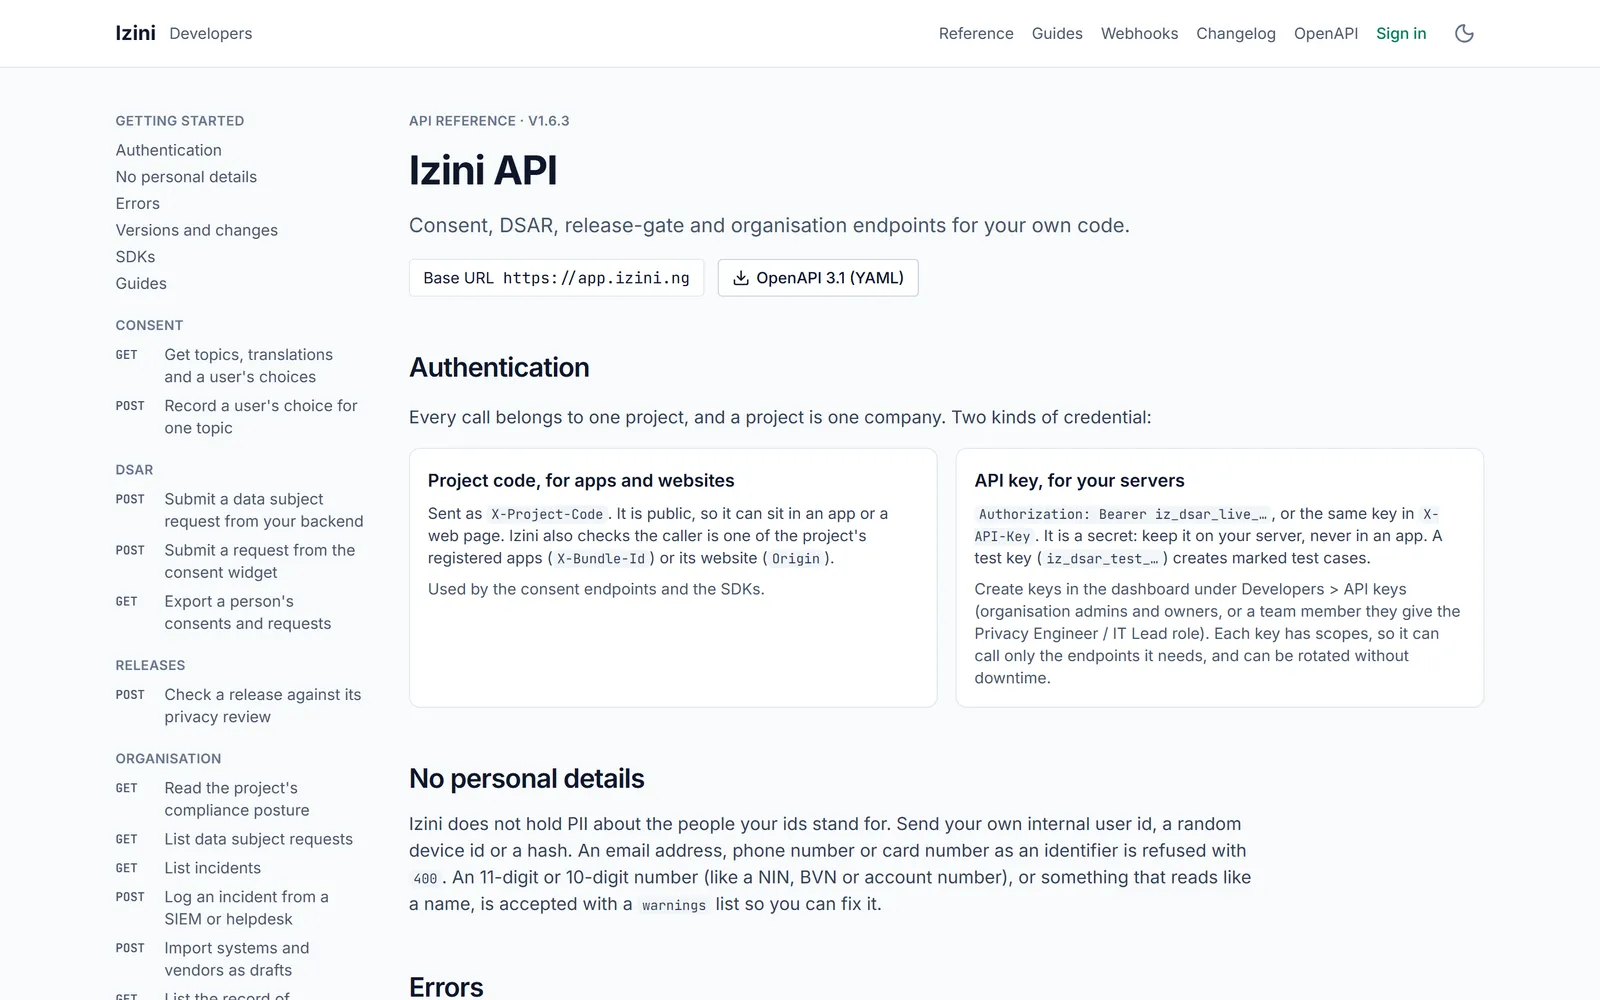
Six things your team can build
Consent in your apps
React Native and Flutter SDKs and a consent API: check consent before a tracker runs, record choices from any channel.
Requests from your backend
Open a data subject request from your own product or support desk through the DSAR gateway, and hear back when it closes.
Incidents from your IT tools
A SIEM, monitoring or helpdesk tool can log an incident directly. With personal data involved, the 72-hour clock starts.
Compliance figures in your dashboards
Read requests, incidents, records, suppliers and impact assessments into Power BI or a GRC tool.
Privacy checks in your pipeline
A release step for GitHub Actions, GitLab or any shell that stops a release until its privacy review is approved.
Alerts in Slack, Teams or Jira
Ready-made n8n and Make recipes turn Izini events into messages, tickets or spreadsheet rows.
13 events, signed and retried
Subscribe to any event, or all of them. Instant events arrive within about a minute; dated ones are checked every hour. Failed deliveries are retried for about a day, and every attempt is logged. Payloads carry IDs, references and dates, never a person's details.
consent.updatedSomeone grants or withdraws consentdsar.receivedA data request arrivesdsar.due_soonA request is due within 7 daysdsar.overdueA request has passed its targetdsar.closedA request is closedincident.createdAn incident is loggedincident.breach_clockThe 72-hour NDPC clock reaches a milestoneincident.ndpc_notifiedThe NDPC has been notifieddpia.completedAn impact assessment is completedpolicy.publishedA privacy policy is publishedvendor.dpa_review_dueA supplier agreement review is duetraining.overdueA training campaign is overduecar.dueThe annual audit return is coming dueSmall enough to read in one go
import { Izini } from 'izini-mobile-sdk';

Izini.initialize({ projectCode: 'YOUR_PROJECT_CODE' });

// Before running a tracker
if (Izini.hasConsent('analytics')) Analytics.start();

// When the user decides
await Izini.updateConsent('analytics', true);// Every webhook is signed: HMAC-SHA256 of "timestamp.body"
const expected = crypto
.createHmac('sha256', process.env.IZINI_WEBHOOK_SECRET)
.update(`${req.get('X-Izini-Timestamp')}.`)
.update(req.body)
.digest('hex');
const received = req.get('X-Izini-Signature-V2') ?? '';Keys, limits and personal data
Scoped keys
Test and live keys, each limited to the scopes it needs, with optional expiry, rotation and a request log.
Predictable limits
Per-key rate limits with standard RateLimit headers, so your client knows when to slow down.
No personal details in
Send your own user ID or a keyed hash. An email address, phone number or card number sent as an identifier is refused.
Plan an integration with us
Tell us what you want to connect. We will show you the endpoints and events that fit, and set up test keys for your trial.
- The endpoints and events for your use case
- Test keys to try it safely
- Answers on limits, security and data handling